A collective cyber-defense call: why AI alone cannot secure essential systems
This week's open letter calls for coordinated support for defenders. Our August 29 report explains the importance of fixing fundamentals and verifying outcomes.

An open letter published this week calls for coordinated cyber defense. TheWrap's August 28 coverage dates its release to Thursday, August 27. OpenAI and technology and security companies are urging practical support for defenders, especially teams protecting essential services with limited resources. This is a call for collective action, rather than an announcement of a single confirmed breach.
What the letter asks for
The signatories warn about increasingly capable AI-enabled attacks and call for prioritizing weaknesses, verified repairs and practical assistance. This is a warning about risk, not a count of incidents that have already happened.
Security starts before software procurement
CISA's August 2024 Secure by Demand guide recommends considering product security during selection, contracting and follow-up after purchase. It suggests questions about security updates, MFA support, security logs and vulnerability reporting. This guidance predates the letter; it is not a new requirement announced this week.
In our assessment, that procurement perspective is useful for smaller organizations too. A team buying an employee application should ask more than how many features it offers. Who owns the repair of a vulnerability? How will the customer know what changed? What evidence will be available if something goes wrong? Turning those questions into clear criteria makes security part of the purchase decision itself.
Software development is part of defense
A CISA and FBI alert published in February 2025 addresses preventing buffer overflow vulnerabilities, including the use of memory-safe languages where appropriate. The broader point is that reducing exposure involves product design and code development as well as tools that observe attacks.
Our suggested starting point is a bounded piece of work that a team can complete: inventory its systems, assign an owner to each, and define how a repair will be verified. An important finding should become an actionable task that somebody can follow through, rather than another notification in a growing queue.
Consider an organizational example. If a problem is found in an internal application, who reviews it, who approves the change, and how does the team establish that the repair has not broken the required workflow? These are proposed response-management questions, not a description of a test we conducted or a local incident we observed.
AI may become part of that process. A more useful success measure is the risk reduced and the effectiveness of the repair, rather than the number of generated answers or alerts. The collective-defense argument becomes meaningful when it leads to a completed, checked improvement in the systems people rely on.
Sources
Founder and editor-in-chief of Kurd Developers. Phone and tech news on YouTube, Instagram and TikTok.
More stories
Apple's Price Ladder: How "Just $50 More" Walks You Into the Pricier Model
You go to buy an iPad mini, pick 256GB, and suddenly you're paying more than an iPad Air. We charted every iPhone, iPad and Mac price on Apple's US store to show where the traps are, and when stepping up is actually worth it.
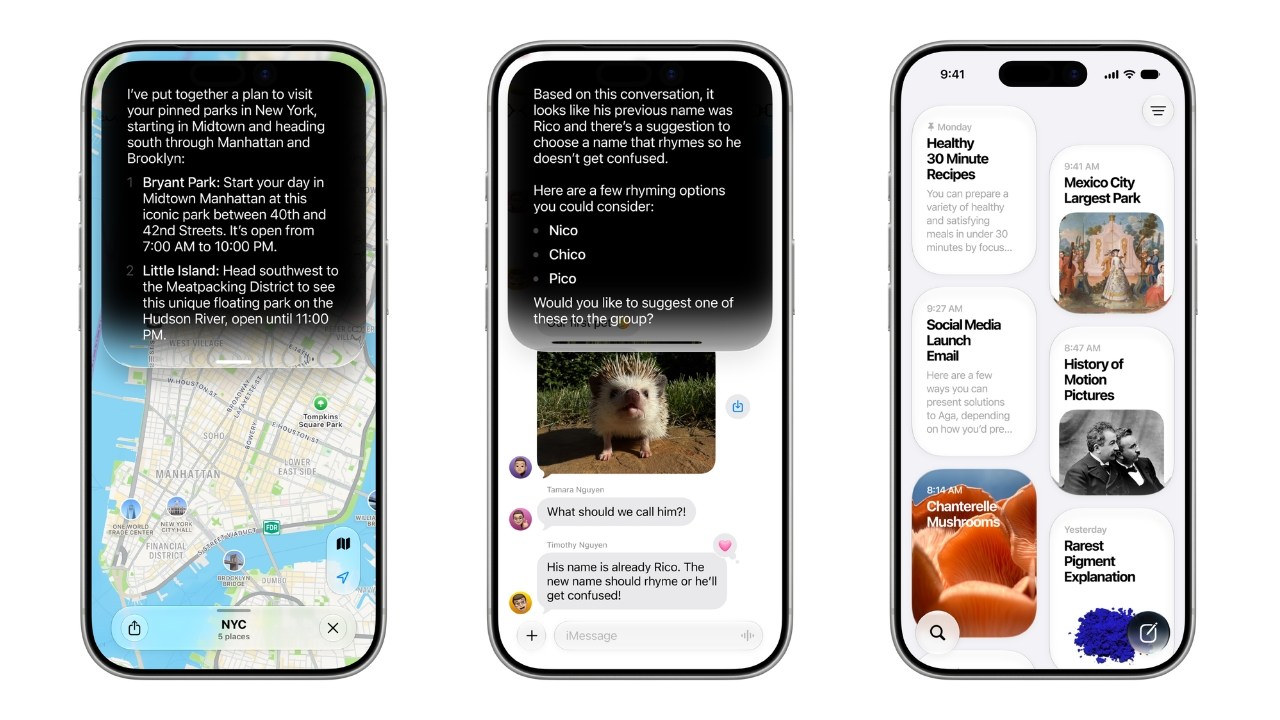
Apple Intelligence Is Coming to China With iOS 27.3, Backed by Alibaba
After more than two years of waiting, Apple says Apple Intelligence will reach iPhone users in China in December, with Alibaba's Qwen model powering parts of Siri.

One text can break your phone: Android's 'SMS of Death' explained
A flaw in Android 12 and later lets a specially crafted SMS drop calls and even make a phone unusable. The fix is in October's security patch.

GTA VI lands November 19: prices, editions and what to know
Rockstar has locked the date: Thursday, November 19 on PS5 and Xbox Series X|S. Standard costs $79.99 and Ultimate $99.99.